
AI Governance
Last reviewed · 4 models · 8 providersSafeguard's AI runs on our own security models: Griffin, Eagle, Lion and Zero. You can also bring your own frontier model, run the whole platform with no AI at all, or run our models inside your own environment.
Commitments
- Customer data is never used to train AI models.
AI modes
Our models
Safeguard models
Griffin, Eagle and Lion, trained by Safeguard for security work, and Zero, which answers with no model weights at all.
Bring your own model
Plug in a frontier model your organization has approved, such as Claude, OpenAI, Cohere or Mistral.
No AI
Zero AI
The platform runs deterministically with no model in the loop.
In your environment
For private cloud, on-prem and air-gapped installs, our models run inside your environment.
Models in use
Griffin
Made by SafeguardRemediation and reasoning.
- Powers
- Reachability analysis
- Fix pull requests
- Natural-language search
- Chat and voice
- Runs in
- Safeguard cloud, or inside your environment
- Used in
- SaaS
- Government
- Private cloud
- On-premises
- Air-gapped
- Data handling
- Customer data is never used to train AI models.
Eagle
Made by SafeguardDiscovery and adversarial review.
- Powers
- Malware and typosquat classification
- Zero-day candidates
- Challenging findings and patches to remove false positives
- Runs in
- Safeguard cloud, or inside your environment
- Used in
- SaaS
- Government
- Private cloud
- On-premises
- Air-gapped
- Data handling
- Customer data is never used to train AI models.
Lion
Made by SafeguardCompliance and narrative.
- Powers
- Evidence mapping
- Audit-ready summaries
- Trust Center copy
- Runs in
- Safeguard cloud, or inside your environment
- Used in
- SaaS
- Government
- Private cloud
- On-premises
- Air-gapped
- Data handling
- Customer data is never used to train AI models.
Zero
Made by SafeguardAnswers without inference.
- Powers
- Semantic analysis turns a question into a query inside the platform
- No weights, no inference, no tokens
- Runs in
- Inside the platform, wherever it is installed
- Used in
- SaaS
- Government
- Private cloud
- On-premises
- Air-gapped
- Data handling
- The question never leaves the platform.
- Customer data is never used to train AI models.
Bring your own model
Providers whose models a customer can bring.
Anthropic
Claude
OpenAI
GPT models
Cohere
Command models
Mistral AI
Mistral models
Google
Gemini models
Meta
Llama models
xAI
Grok models
Your own model
Any model of your choice
An OpenAI-compatible endpoint, a self-hosted open-weight model, or a private deployment in your own cloud.


All product names and logos are trademarks of their owners; use does not imply endorsement.
Governance practices
Human oversight
Autonomous fixes arrive as pull requests that a person reviews before they merge, and autonomous remediation is off until you turn it on.
Agent identity
Every AI agent acts under its own identity, separate from any person's account. A tenant admin decides which roles each agent holds; an agent can never hold platform, tenant admin or auditor authority, and every change to an agent's access is written to the audit log.
Where agents run
Agents work in isolated environments: sandboxes, cloud browsers, cloud computers and a cloud CLI. Each runs in its own container with a fixed set of permissions, and none exposes a remote-control port. With the local runner, the CLI works on your own machine instead: it pulls the repository there, scans it there and sends back only encrypted results, over polling with no inbound connection.
Agent monitoring
Each AI agent acts under its own identity with the roles a tenant admin gives it, and every change to an agent's access, including refused attempts, is written to the audit log. Which tools an agent may call is set per tool, so a reviewer can see and limit what each agent can do.
AI security and compliance
Safeguard treats AI assets as first-class objects: it inventories models, agent skills and agent configurations with their tool access, scans model files for malware, and maps AI controls to ISO/IEC 42001, the NIST AI RMF and the EU AI Act.
Agent runtime protection with Guard
Safeguard Guard sits in front of models and MCP tool traffic at runtime and checks for prompt injection, jailbreaks and secret or personal-data leaks, in monitor mode or enforce mode. Guard is in early access.
Private mode
Private mode keeps searches and conversations from being stored.
Your choice of model
AI mode is set per tenant: Safeguard models, your own model, or no AI at all.
Frameworks
All frameworks
ISO/IEC 42001:2023
In Progress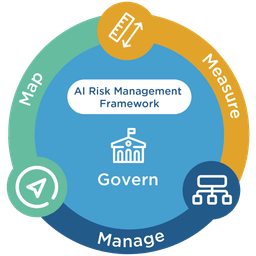
NIST AI RMF 1.0
Compliant
EU AI Act
Compliant
NIST AI RMF graphic: N. Hanacek/NIST. EU emblem: European Union. It marks legislation of the European Union and does not mean the EU is connected with this organisation.